One engine, two speeds.
Scandium scans continuously so you catch regressions in hours. Our senior pentesters handle the business logic and chained exploits scanners will never find.
Your perimeter, watched in real time.
Full-spectrum coverage in a single engine: networks, web apps, systems, cloud; scanning on your schedule or on every deploy. Findings land in a live dashboard instead of a static PDF, with remediation guidance built in.
One engine, every surface
Networks, web apps, systems, and cloud in a single workflow, with no point-tool sprawl.
Scans that never sleep
Scheduled recurring scans plus real-time alerts. Retests on-demand after every fix.
Remediation, not just CVE IDs
Every finding ships with an exploit snippet, reproduction steps, and clear fix guidance.
Fuel for deep engagements
Scandium surfaces low-hanging fruit; your pentesters go where scanners can't reach.
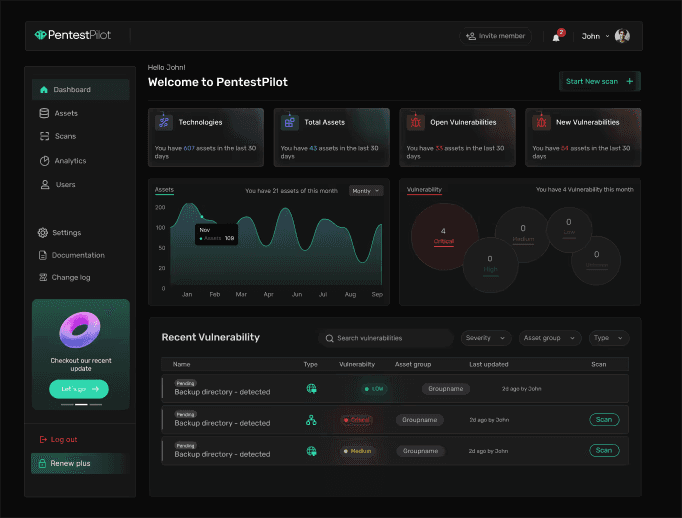
Scanners are fast. Humans are smart.
Choose both.
Competitors force you to pick one. Our engagements ship with both: automated coverage at scale paired with senior pentesters who chase the exploits machines will never find.
Scandium Continuous Scan
Runs 24/7 across every asset. Catches known CVEs, misconfigurations, exposed services, and regressions before they reach production.
- Known CVEs & misconfigurations
- TLS / cert / header hygiene
- Cloud posture drift
- Dependency & supply-chain alerts
Expert-led, hand-picked pentesters
Scoped engagements that go where scanners can't: business logic, chained exploits, privilege flows, auth edge cases, race conditions.
- Business logic & auth flows
- Chained exploits & privilege escalation
- Race conditions & side channels
- Threat modeling & attack narratives
Continuous coverage. Expert-led pentests.
Move from once-a-year snapshots to a live security posture. Book a scoping call and we'll quote your first engagement within 48 hours.